They model realistic situations the place attackers work together with cryptographic systems somewhat than simply observing them. Encrypting delicate https://northfloridahouse.com/cqr-company-a-new-look-at-cybersecurity-for-business.html assets such as databases, storage volumes, and backups must be a default operation managed by automation, not guide processes. Safety groups ought to leverage instruments that provide real-time monitoring, alerting, and self-healing for cryptographic controls so that deviations from policy or greatest practices set off instant responses. Regular rotation and timely destruction of old or potentially uncovered keys scale back danger and comprise the impression of key compromise.
Brute Drive Assault
Algorithms corresponding to MD5 or unsalted SHA-1 enable attackers to test giant numbers of candidate passwords rapidly once a hash database is obtained. The failure is not within the breach itself, however in the inability of the hashing design to gradual or stop password restoration after publicity. Repository containing implementation of assaults on trendy public key cryptosystems and symmetric key ciphers. Therefore, whereas attacking an encryption algorithm, the adversary usually has two major targets, looking for the secret code or discovering the open text that meets the encryption code. A robust system additionally attempts to determine proof of malicious exercise and restrict the impact of any attacks.
Documentation of those processes strengthens compliance evidence and supports continuous enchancment. Groups ought to solely depend on totally reviewed libraries with a strong reputation and group support. Keep Away From creating customized cryptographic code, as such options are notoriously prone to subtle and devastating flaws. Common scanning of the software stack, together with a disciplined patch administration course of, limits the assault surface.
Publication History
Cryptographic failures are vulnerabilities that happen when functions poorly implement or use cryptography, resulting in the publicity of sensitive information. The document outlines various cryptographic attacks, together with passive and lively attacks, cryptographic assaults, and software-based assaults, emphasizing the importance of understanding these varieties for safe system design. It additionally covers encryption strategies similar to Hill Cipher and Playfair, the Euclidean algorithm for GCD calculation, and details on the Knowledge Encryption Standard (DES) and its rounds. Additionally, it discusses block cipher modes, SHA-512 hashing, message authentication codes, public key distribution methods, X.509 certificates fields, and the Kerberos authentication protocol. Fashionable digital methods rely on cryptography to make sure secure communication—but vulnerabilities in implementation can open the door to severe attacks. In this course, Cryptographic Purposes and Attacks, you’ll learn attacks towards cryptographic protocols and applications.
Enforce Sturdy Key Lifecycle Administration
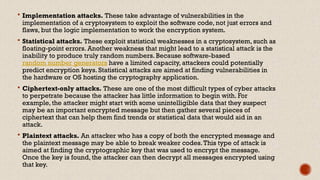
Accordingly, it’s potential to differentiate such attacks as an encrypted-text-based approach. It occurs when the adversary has ciphertexts of various unknown open texts encrypted with the same key. The task of the cryptanalyst is to obtain the open text of extra messages or accept the key used within the encryption (Zimba et al., 2020).
These failures are tough to detect because the cryptographic algorithms themselves remain mathematically sound. Using weak or outdated cryptographic algorithms stays a common supply of failure in safety architectures. Algorithms corresponding to MD5, SHA-1, and RC4 have well-documented vulnerabilities that attackers are able to exploit utilizing inexpensive computational assets. Reliance on these legacy algorithms offers only limited safety and exposes knowledge to recognized attacks which were sensible for years. You’re being examined in your capability to establish vulnerabilities, suggest acceptable countermeasures, and explain the relationship between assault vectors and defensive mechanisms. These ideas seem repeatedly in questions on protocol safety, algorithm selection, and system hardening.
- Furthermore, it was realized that a truly dependable encryption system should remain safe even when an opponent totally recognizes the cryptographic algorithm.
- To improve detection and response, Cloud Community Analytics supplies traffic visibility and anomaly detection that may help determine suspicious patterns in maintaining with downgrade attempts, MITM probing, or credential abuse.
- Here are a few of the ways in which organizations can ensure they keep away from cryptographic failures.
- Failure at any stage of the data transmission path leaves organizations open to interception assaults like sniffing, replay, or man-in-the-middle.
- The cryptographic attacks could be categorized according to the quantity and kind of knowledge out there for cryptanalysis by the adversary.
Accordingly, it’s essential to detect such an assault after which restrict it to be assured that the harm caused might be minimized. Lapses in any of these practices open the door to key leakage or misuse, often enabling attackers to decrypt or forge sensitive knowledge while not having to break the underlying encryption itself. Organizations must recognize that cryptographic strength degrades over time as extra analysis uncovers weaknesses and as computational power will increase. Without a deliberate strategy to evaluate and update cryptographic algorithms in deployed techniques, what was as quickly as “secure” can become obsolete. Risk modeling should include cryptographic belongings, contemplating potential attackers, abuse cases, and failure modes related to cryptography.
It also simplifies enterprise-wide enforcement of security insurance policies similar to disabling legacy protocols and guaranteeing robust cryptographic configurations across distributed utility environments. All knowledge transmissions involving sensitive information should use secure transport protocols, corresponding to trendy versions of TLS with robust cipher suites and strict certificates validation. Keep Away From legacy options or permitting insecure downgrades, as these create clear paths for site visitors interception or active manipulation. End-to-end encryption should be enforced even over trusted networks to counteract attainable internal threats. Security professionals ought to mandate the utilization of current and broadly accepted cryptographic algorithms, similar to AES for encryption and SHA-256 or stronger for hashing.
The encryption code key is contained in a categorized form, and the other parameters of the encryption system can be disclosed without reducing the algorithm’s strength. In Any Other Case, it’s reasonable to imagine that the adversary knows everything in regards to the encryption system in use except the relevant keys when assessing encryption safety. The Kerckhoffs principle focuses on establishing the safety of algorithms and protocols independently of their secrecy; openness cannot affect safety (Lou et al., 2021).
Safety groups should leverage configuration validation tools, automate deployment of hardened settings, and monitor environments for drift from established secure baselines. A brute pressure attack includes trying all attainable keys until the right one is found. Routine safety audits that specifically assess cryptographic controls are essential for figuring out gaps in protection before they lead to incidents. This involves regular external and inside penetration testing, vulnerability scanning, and evaluation of code and infrastructure for adherence to cryptographic insurance policies.
